Overview
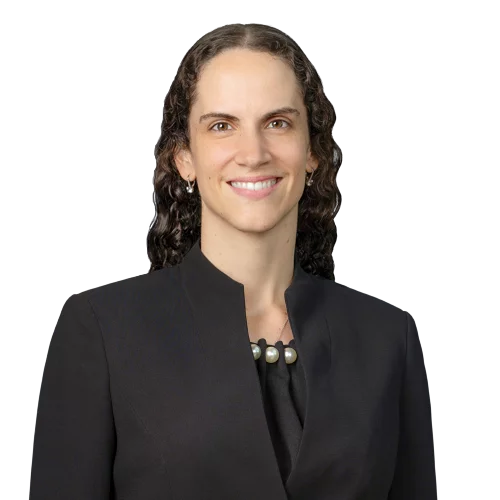
Trish Carreiro is an experienced data lawyer who focuses on minimizing the risks associated with data collection, use, transfer, storage, and disclosure. She is certified by the International Association of Privacy Professionals as an artificial intelligence governance professional (AIGP), certified information privacy professional (CIPP/US), certified information privacy manager (CIPM), and fellow of information privacy (FIP), and she is a prior multiterm co-chair of the IAPP's South Florida chapter.
Trained as a business litigator, Trish combines her litigation skills with technical proficiency in cybersecurity, privacy, and artificial intelligence to advise highly regulated businesses on privacy, cybersecurity, and artificial intelligence governance compliance, program management, and related prophylactic measures; negotiate data processing terms and technology agreements; respond to cybersecurity incidents; advise on proactive risk management regarding new and emerging technologies and data uses; and defend against privacy, cybersecurity, or data-related putative class actions and regulatory inquiries.
Insurers and financial services entities make up a majority of Trish’s practice. She helps insurers, broker-dealers, producers, and investment advisers navigate the morass of state and federal privacy laws to market their products in new and innovative ways, streamline their privacy compliance, adjust to changing laws, digitize their application process, increase consumer engagement, respond to cybersecurity incidents, apply new technologies and data to underwrite their risk, incorporate artificial intelligence into their business, respond to regulatory inquiries, and defend against putative class actions.
From drafting the necessary notices and consents, to developing the process for presenting and recording authorizations, to designing full compliance programs and governance structures, Trish uses her experience to propel the industry forward.
In the health care sphere, Trish has been advising clients and publishing thought leadership for nearly a decade. When COVID-19 struck, Trish was one of the first to begin writing about the privacy and cybersecurity challenges facing the health care industry and, more important, how to navigate them. She has represented numerous health care providers in class action breach litigation, data breach response, and post-breach Office for Civil Rights and attorneys general investigations, and she has drafted comprehensive HIPAA compliance programs for HIPAA-covered entities and business associates.
A recognized thought leader, Trish uses her litigation perspective to guide clients to both avoid, and effectively handle, privacy and cybersecurity litigation. She is a frequent speaker on these topics, and her insights have been featured in publications including Bloomberg Health Law & Business, Law360, Law.com, Corporate Counsel, Today’s General Counsel, InsideCounsel, The Cybersecurity Law Report, Data Breach Today, Health IT Security, Healthcare IT News, Healthcare Infosecurity, Life Annuity Specialist, Fierce Healthcare, Daily Business Review, Miami Herald, Dark Reading, STAT, and Tampa Bay Business Journal.
When we got off the call, the whole room simultaneously broke out in praise for how great it is working with Trish. She exhibits clear, collaborative, decisive, understanding of our business situation."
Experience
Artificial Intelligence and Emergent Technologies
Advised businesses of varying sizes regarding procurement, use, and governance of artificial intelligence, including analyzing risks and risk mitigation measures, building governance structure, negotiating contracts, and drafting notices, consents, and associated policies and procedures for various use cases, such as meeting notetaking, locating/summarizing policy information, marketing content creation, and chatbots for customer service and other consumer engagement initiatives.
Counseled businesses across industries regarding use of various technologies and methods for increasing digital engagement.
Privacy and Cybersecurity Class Action Litigation
Secured the voluntary withdrawal of multiple putative class actions against an insurance producer, without any settlement payments or defensive court filings.
Advised one of the nation's largest banks on possible causes of action, defenses, class action strategy, and litigation options following a nationwide data breach.
Advised large, publicly traded financial institution regarding multiple data breach class actions.
Settled multiple data breach class action demands for no payment and without a single court filing.
Defended multiple health care providers in class action breach litigations stemming from cybersecurity attacks.
Represented various entities in responding to consumer allegations of privacy violations, including in relation to website technologies such as Meta Pixel and cookies.
Privacy Compliance: Financial Institutions
Advised multiple large brokerages regarding privacy policy program needs, including privacy notices, data processing agreements, and internal policies and procedures.
Advised large life insurers and affiliated producers regarding privacy compliance throughout development of fully electronic automated underwriting application, including negotiating contractual agreements with third-party service providers, developing procedures for operationalizing and demonstrating privacy compliance, and drafting privacy policies, procedures, notices, and authorizations.
Counseled various financial institutions, including insurers, producers, and mortgage servicers, regarding compliance with privacy laws such as the Gramm-Leach-Bliley Act (GLBA), the California Consumer Privacy Act (CCPA), the Telephone Consumer Protection Act of 1991 (TCPA), the CAN-SPAM Act of 2003, the Telemarketing Sales Rule, the Fair Credit Reporting Act, the Health Insurance Portability and Accountability Act (HIPAA), and National Association of Insurance Commissioners (NAIC) model laws, as applicable.
Advised multiple insurers regarding notices and consents needed when seeking information about applicants/insureds from third parties, or seeking to share applicant/insured information with third parties for transactional or marketing purposes; privacy compliance regarding contacting applicants/insureds via varying means throughout the insurance application process; development of mobile applications; handling of consumer data subject requests to know, correct, delete, or limit sharing; cybersecurity obligations; and responding to, and preparing for, examinations regarding cybersecurity and privacy practices.
Counseled financial institutions regarding intersection of the GLBA and state privacy laws, such as the CCPA.
Advised large financial entities regarding contractual privacy provisions, privacy compliance, and cybersecurity insurance coverage.
Drafted privacy policies, associated notices, and privacy request processing procedures for organizations across industries and regimes.
Privacy Compliance: Health Care
Drafted a comprehensive HIPAA compliance program, including drafting associated policies and procedures, for a HIPAA-covered entity.
Managed breach response for various HIPAA entities, including covered entities and business associates, throughout breach investigation, required reporting and notifications, and any associated litigation.
Advised business associates regarding compliance with the CCPA, including drafting necessary privacy notices and establishing procedures for processing associated privacy requests.
Advised health care entities regarding privacy compliance needs, including privacy practices, mobile application and website terms, and internal policies and procedures.
Privacy Compliance: Privacy and Cybersecurity Program Management
Advised multiple Fortune 500 companies regarding adjustments needed to comply with new state privacy laws.
Designed and implemented a privacy program for a large U.S.-based retailer.
Created privacy policies and website terms of use.
Draft and negotiate data processing agreements and contractual provisions for vendor management.
Draft internal privacy and cybersecurity policies and procedures, including breach response, data retention/destruction, and others.
Advise regarding privacy and cybersecurity risk management, including key contractual provisions and policy best practices.
Data Breach Response
Represented companies in investigating and responding to phishing, ransomware, business email compromises, and wire diversion schemes.
Executed data breach response for companies of all sizes, including managing forensic investigation, data mining, and required reporting to regulators, law enforcement, media, and consumers for breaches of CPNI, GDPR data, and other personal information. Representative entities include insurers, producers, health care providers, retailers, telecommunications carriers, and businesses large and small.
Represented health care providers throughout post-breach investigations by the Office for Civil Rights and attorneys general.
News & Insights
News
Publications
Speaking Engagements
"Key NAIC (A), (E), and (H) Committee Initiatives: A Discussion With NAIC Leaders," ALI CLE Conference on Life Insurance Company Products, Washington, D.C. (November 5, 2026)
"Practical AI Governance," Carlton Fields (October 22, 2026)
"Tech and Transformation: An AI Industry Update," National Association for Fixed Annuities Annuity Leadership Forum, Washington, D.C. (June 22, 2026)
"The Latest Cyber Threats and Coverage Issues," Carlton Fields Client Presentation (June 17, 2026)
"Wiretapping Litigation Update," American Council of Life Insurers Privacy and Cybersecurity Committee (April 16, 2026)
"Getting It Right: The Dos and Don'ts of AI Implementation for Life and Annuity Distribution," National Association for Fixed Annuities (February 19, 2026)
"Innovations in Life Insurance and State Insurance Regulatory Initiatives," ALI CLE Conference on Life Insurance Company Products, Washington, D.C. (November 13, 2025)
"U.S. v. Mexico Cybersecurity and Privacy: Threats, Law and Incident Response," International Association of Privacy Professionals (November 4, 2025)
"Insuring Compliance: Managing Insurance Industry AI and Privacy Compliance," International Association of Privacy Professionals Privacy. Security. Risk., San Diego, CA (October 30, 2025)
"Third-Party Risk Management," American Council of Life Insurers Annual Conference, Nashville, TN (October 16, 2025)
"Mitigating Emerging Technology Implementation Risks," National Alliance of Life Companies Fall Conference, Mont-Tremblant, Canada (September 12, 2025)
"Smooth Sailing: Managing Risk and Cost in Defending Class Actions," Association of Corporate Counsel South Florida 15th Annual CLE Conference, Hollywood, FL (September 5, 2025)
"AI, Ag Tech, and the Law: Protecting Your Business and Farm Data," Tech Hub LIVE Conference and Expo, Des Moines, IA (July 22, 2025)
"Navigating Third-Party Management: A Legal Perspective," American Council of Life Insurers Compliance & Legal Conference, New Orleans, LA (July 14, 2025)
"Getting It Right: The Dos and Don'ts of AI Implementation for Annuity Distribution," National Association for Fixed Annuities Annuity Leadership Forum, Washington, D.C. (June 24, 2025)
"Unlock the Power of Trust: How Prioritizing Data Privacy Can Drive Growth, Protect Your Brand, and Future-Proof Your Business in the New AI Era," Broward Workshop Technology Committee (May 7, 2025)
"Getting It Right: The Dos and Don'ts of AI Implementation for Life and Annuity Distribution, Part I: Sorting Through the Noise," National Association for Fixed Annuities (February 25, 2025)
"The Latest Cybersecurity, Privacy, and Data Rights Developments," ALI CLE Conference on Life Insurance Company Products, Washington, D.C. (November 8, 2024)
"Careers in Privacy," Stetson University College of Law (October 24, 2024)
"Privacy Class Action Claims Impacting the Life Industry," Association of Life Insurance Counsel Fly-In, New York, NY (October 17, 2024)
"Cybersecurity Update," National Association for Fixed Annuities Annuity Leadership Forum, Washington, D.C. (June 24, 2024)
"Litigation Risk: What Every Insurer and Innovator Needs to Know," Global Insurance Symposium, Des Moines, IA (April 16, 2024)
"Privacy, Cybersecurity, and Artificial Intelligence," Journal of International Law Symposium, University of Florida College of Law (March 1, 2024)
"The Latest Privacy Developments," Integrity Marketing Compliance Summit, Washington, D.C. (February 27, 2024)
"Preparing for Cybersecurity and Privacy Success in 2024," National Association for Fixed Annuities (February 8, 2024)
"Cybersecurity and Data Privacy and Rights Management," ALI CLE Conference on Life Insurance Company Products, Washington, D.C. (November 2, 2023)
"What Does AI Mean for Your Business?," Artificial Intelligence Forum, Greater Miami Chamber of Commerce, Miami, FL (October 25, 2023)
"Privacy, Cybersecurity, and Artificial Intelligence for Startups," Nova Southeastern University, Berger Entrepreneur Law Clinic (October 13, 2023)
"Privacy and the Use of AI," Law and Compliance All Hands Meeting, Symetra Life Insurance Co. (October 12, 2023)
"The Good, the Bad, and the Ugly: AI in the Life Insurance Industry," Association of Life Insurance Counsel Fly-In, Cincinnati, OH (October 3, 2023)
"Website Tech Fueling Privacy Litigation: How to Reduce Your Risk," Carlton Fields (April 17, 2023)
"Cybersecurity Fraud Threats: Attacks Against Insurers, Contract Owners, and Retirement Account Holders," Association of Life Insurance Counsel Regional Insurance Counsel Roundtable (October 25, 2022)
"Financial Services Cyber Fraud: The Latest Risks and Best Responses," Carlton Fields (October 20, 2022)
"The Latest Cyber Threats and Coverage Issues," Carlton Fields (June 28, 2022)
"An Overview of Life Insurers' Privacy and Cybersecurity Requirements," Carlton Fields (June 21, 2022)
"Digital Marketing: Thriving, Surviving, or Dead on Arrival?," International Association of Privacy Professionals (March 2022)
"Data Breach Litigation," Global Aesthetics Conference (November 2021)
"HIPAA Breaches," Miami Cosmetic Surgery & Aesthetic Dermatology Symposium (August 2021)
"Decision-Making With FAIR: Quantification and the Rise of Class Action Lawsuits," FAIR Conference (October 2020)
"Privacy Leaders Circle: Miami," Truyo (July 9, 2020)
"Privacy Policy and Terms of Use Basics for Start Ups," Nova Southeastern University College of Law (March 2020)
"Evaluating Cyber Insurance Using the FAIR Doctrine," Legal Services Information Sharing and Analysis Organization (May 2019)
"Using FAIR to Optimize Your Cyber Insurance Coverage," FAIR Conference on Information Risk Management (October 2018)
"Data Breach Litigation: Recent Trends and Developments," The Knowledge Group (June 2018)
"Cyber & Law: It's Really About the Money," Evolver (January 2018)
"Which Insurance Would Cover a Breach-Related Injury?," HealthcareInfoSecurity (October 2017)
"Cyber Risk and Liability Insurance: What Is It and Why You Need It," The Knowledge Group (October 2017)
"She Leads: Women in the Law," Quinnipiac University School of Law (November 2016)
"Cybersecurity Litigation and the Role of Cyber Insurance," Connecticut Law Tribune (September 2015)
View less
Multimedia
Recognition
Honors & Recognitions
The Best Lawyers in America: Ones to Watch (2024–2025)
No aspect of this advertisement has been approved by the highest court of any state. See Awards Methodology.
Professional & Community Involvement
Professional & Community Involvement
Trish is active in several privacy and insurance industry organizations. She is a member of the International Association of Privacy Professionals, where she participates in its Women Leading Privacy initiative, and the Association of Life Insurance Counsel. She serves on the Education Committee of the National Association for Fixed Annuities, the Artificial Intelligence Working Group of the Insured Retirement Institute, and the Technology and Innovation Committee of the Greater Miami Chamber of Commerce. In the community, she is a member of United Way Women United.
Her past service includes co-chairing the International Association of Privacy Professionals' South Florida KnowledgeNet chapter and serving on the planning committee for the National Association for Fixed Annuities' Leadership Forum. She also served on the Cyber Insurance Workgroup of the FAIR Institute, a nonprofit dedicated to advancing cyber risk measurement and management, and she is a past LCLD fellow. In Connecticut, she served on the executive committee of the Connecticut Bar Association's Women in the Law Section and represented Hartford's District 12 in its House of Delegates.
Beyond the Bio
Trish leads the firm's cybersecurity, data privacy, and artificial intelligence work. Her prior experience includes internships with the U.S. Department of Justice Criminal Division's Fraud Section, the U.S. Securities and Exchange Commission Division of Enforcement, the New York State Attorney General's Medicaid Fraud Unit, and the Connecticut Commission on Human Rights and Opportunities. She is active in efforts to support women in the privacy profession.
Related Capabilities
Bar Admissions
Court Admissions
Certifications
Artificial Intelligence Governance Professional
Certified Information Privacy Manager
Certified Information Privacy Professional
Fellow of Information Privacy
Education
J.D., New York University School of Law
B.A., Duke University
Languages
- Portuguese
- Spanish